COGNNA's MDR for Microsoft runs your security operations on Defender XDR and Sentinel, 24/7/365. Agentic AI triages, Guardians respond inside your tenant.
No rip-and-replace.
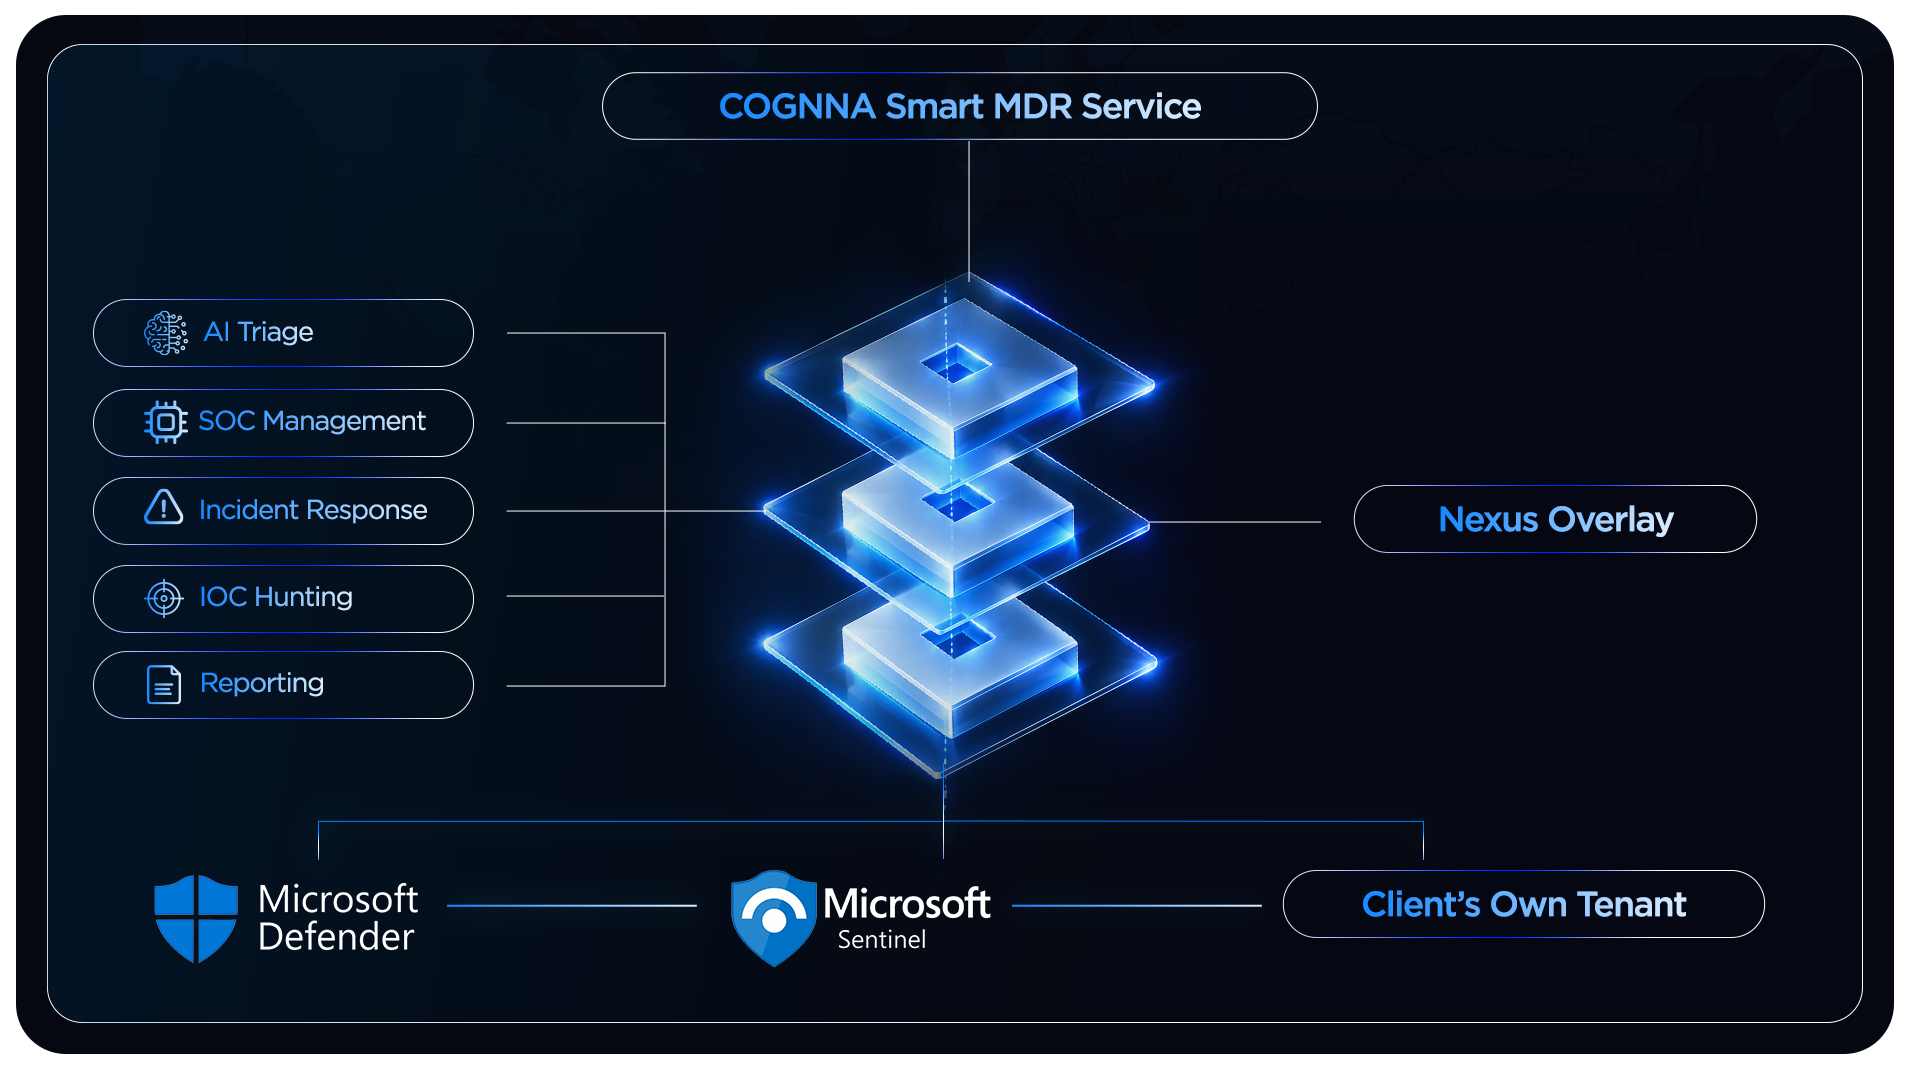
Defender XDR and Sentinel licenses are paid for, but rarely operated to their full potential. COGNNA Smart MDR for Microsoft, powered by Nexus, runs the security operations across your Microsoft stack, turning your existing investments into measurable outcomes.

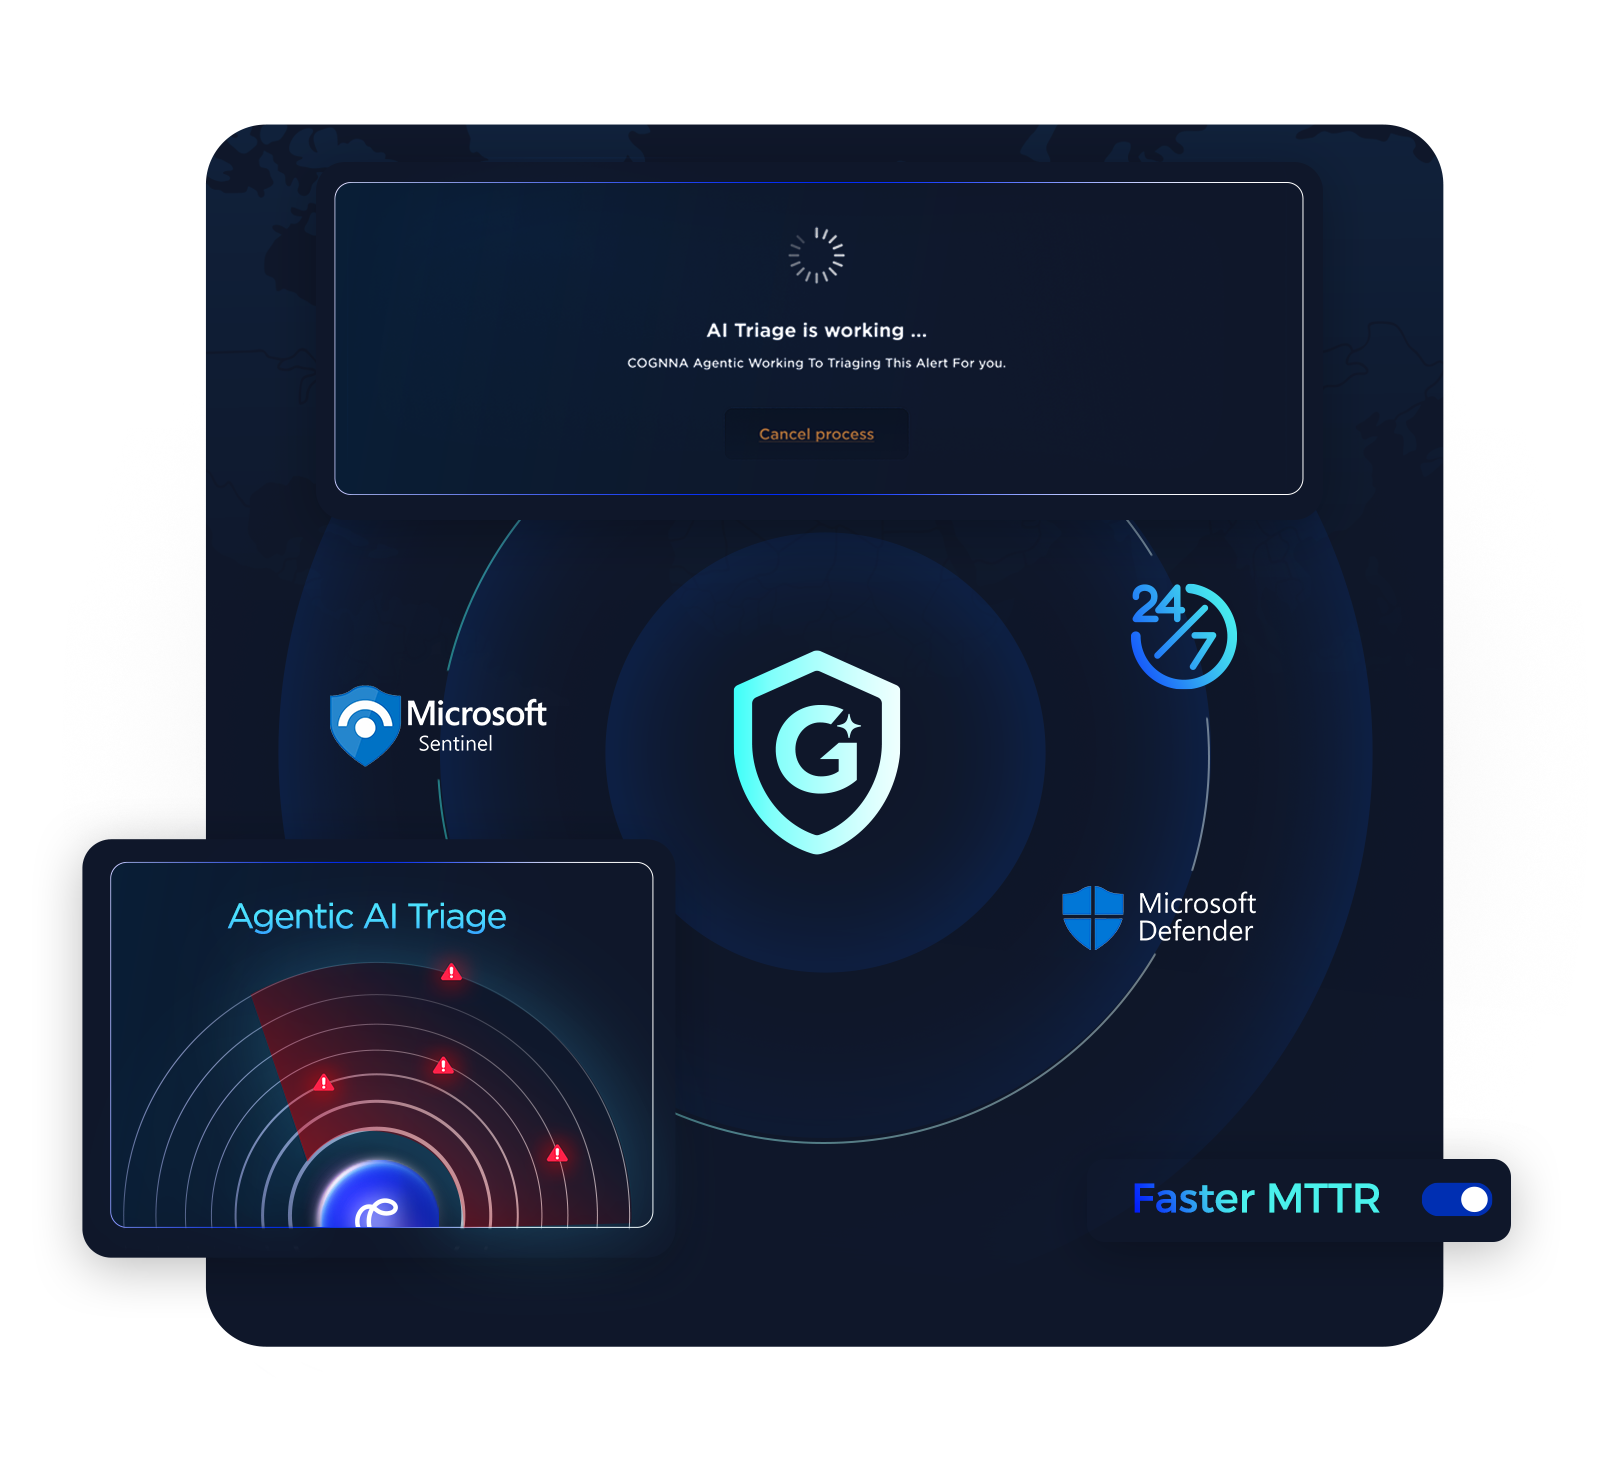
Two analysts cover roughly 80 hours of a 168-hour week, while Defender and Sentinel alerts keep growing. COGNNA's Microsoft MDR runs your security operations 24/7/365. Agentic AI triages alerts, so that Guardian Experts focus on the real threats.
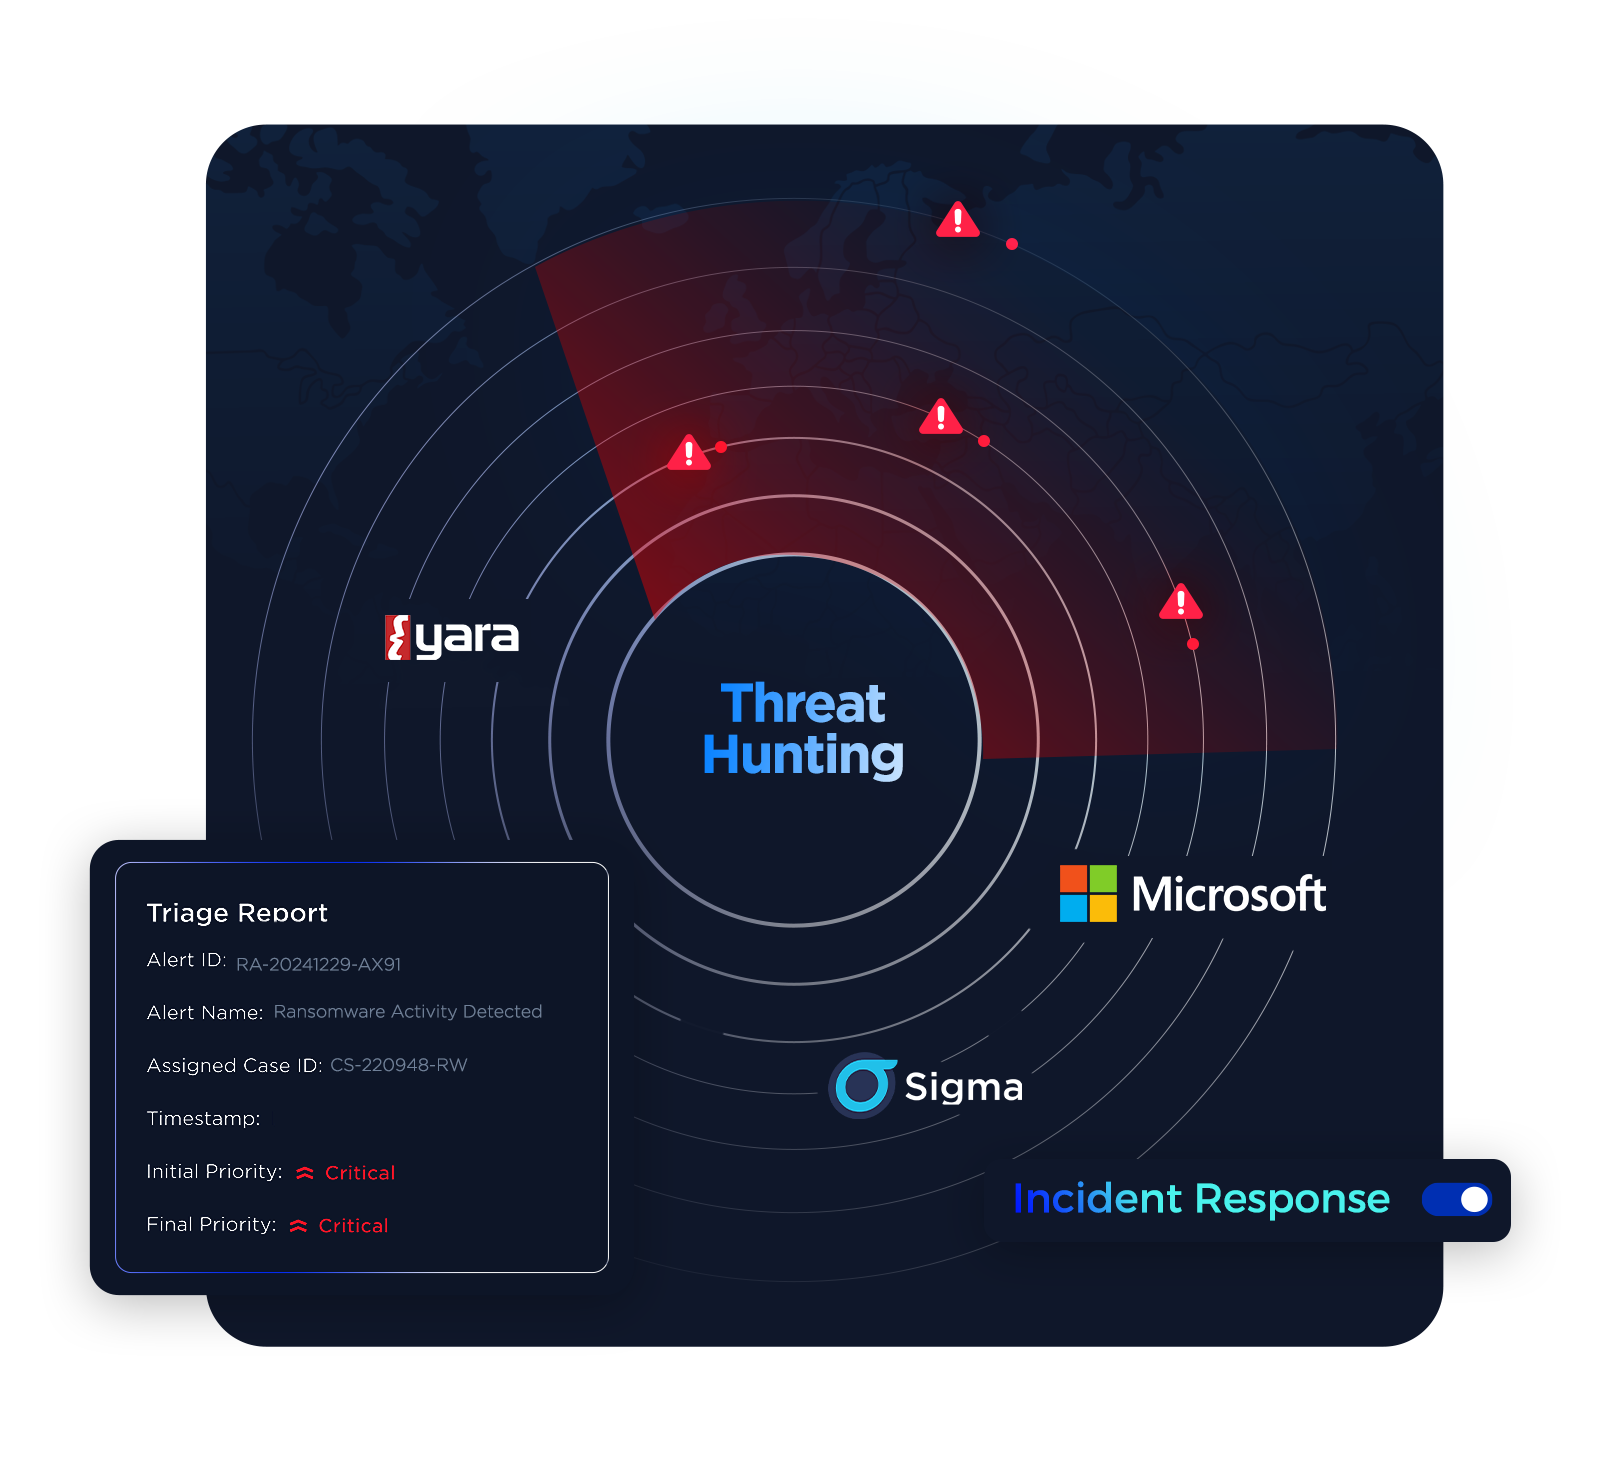
Microsoft surfaces the threat, but someone still has to contain it and hunt for what never triggered an alert. COGNNA's MDR for Microsoft owns incident response inside your own tenant, with Guardian Experts hunting proactively for threats before they spread.
90%
Faster Threat Validation
80%
Reduction in MTTR
24/7
Guardians Coverage
.png)
MDR for Microsoft is a managed detection and response service built on Microsoft Defender XDR and Microsoft Sentinel. With COGNNA Smart MDR for Microsoft, Guardian Experts and Agentic AI monitor, investigate, hunt, and respond to threats 24/7/365 inside your own tenant. You get full value from the Microsoft stack you already own.
No. If you already run Sentinel with Defender XDR, COGNNA's Microsoft MDR connects directly to your existing workspace. If you run Defender XDR only, you have two options. COGNNA can help you set up a Sentinel workspace, or COGNNA Nexus' built-in SIEM and Data Lake can run alongside your Defender XDR.
No rip-and-replace is required. COGNNA MDR for Microsoft works on your existing Defender XDR, Sentinel, and connected data sources. If you ever leave, your workspace, detection rules, workbooks, and incident history stay with you.
COGNNA tunes data collection rules to reduce ingestion volume and noise without sacrificing the visibility your detections depend on. This optimized log ingestion leads to reduced data costs.
Access is delegated, least-privilege, and time-scoped, with MFA and conditional access on every path. Every Guardian action is logged in your own activity log and attributed to a named person. You can view, and audit access at any time.
COGNNA ensures rapid response by combining AI triage, AI-led detection and threat validation with dedicated Guardian experts. Nexus continuously prioritizes and investigates security events across your stack, enabling faster threat identification, quicker containment, and reduced Mean Time to Respond (MTTR).